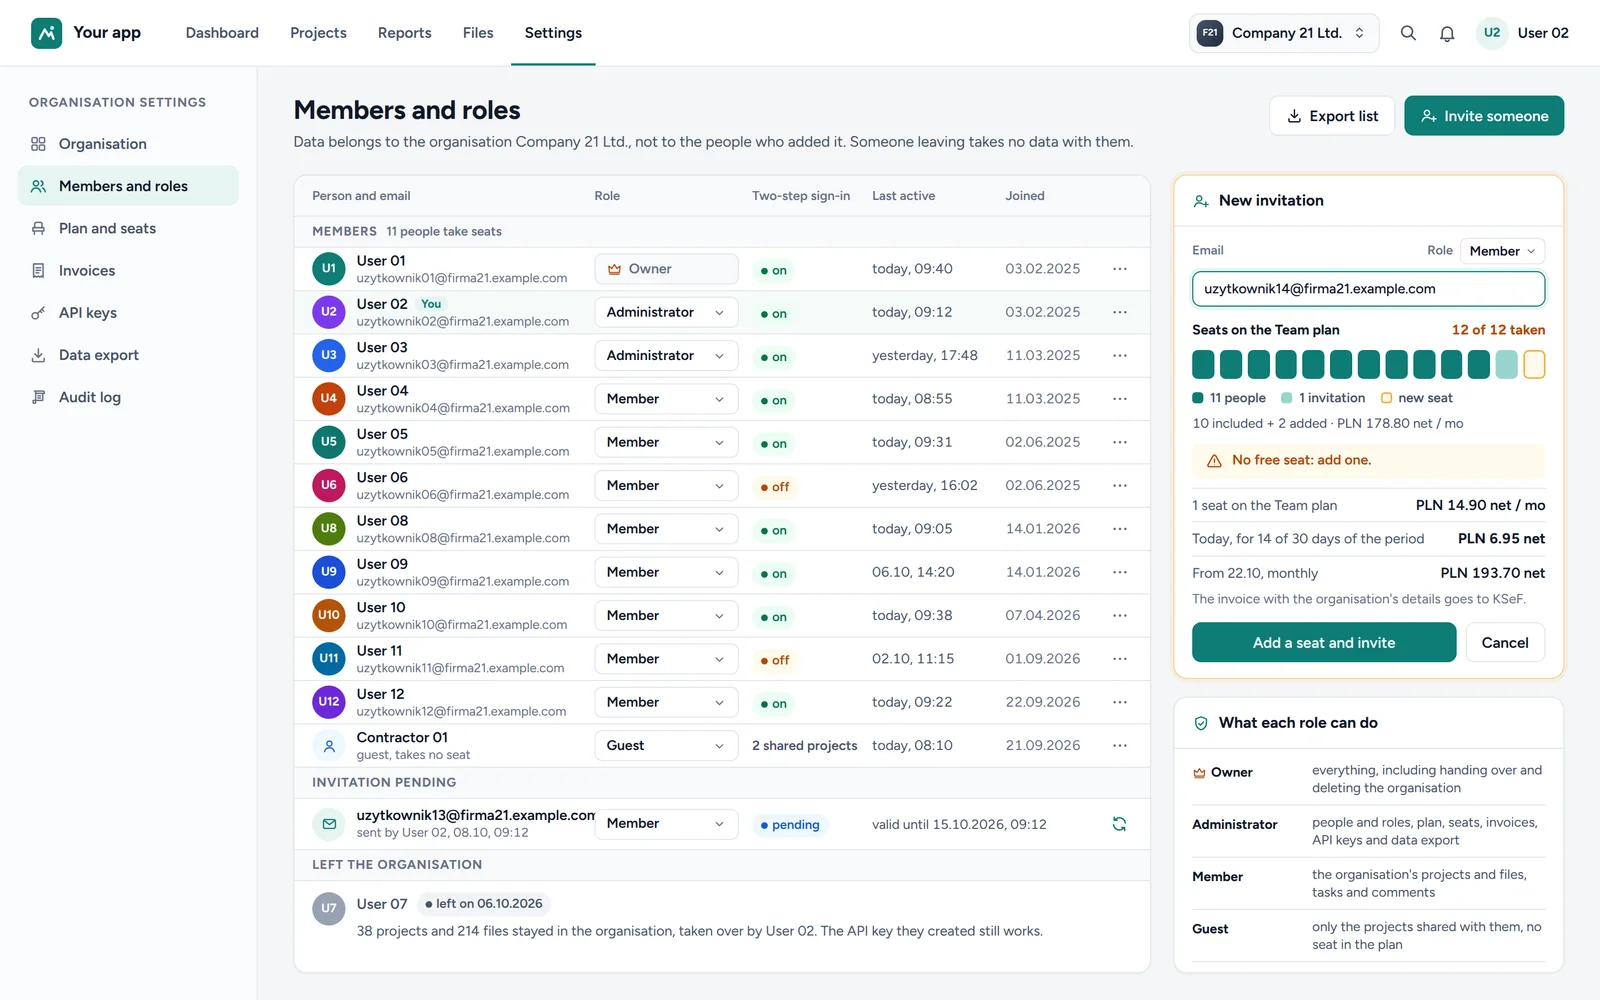

Broken access control stays at number one in the OWASP Top 10:2025, and 100% of the applications tested had some form of it. OWASP sets three rules: access control only works in server-side code the user cannot modify, everything but public resources is denied by default, and users read and change only the records they own.
Roles on a B2B platform
| Role | Sees | Changes |
|---|---|---|
| Client buyer | their company's prices, limit and invoices | places orders |
| Client manager | as the buyer | approves the company's orders |
| Sales rep | clients' price lists, limits and invoices | price lists, discounts, orders for clients |
| Finance | price lists, limits, invoices and receivables | the credit limit |
How we settle the roles
We agree roles with you before the first screen and write them into a role matrix, so every department sees only its own data and features, and a client in a B2B panel sees only their own orders and invoices. Before launch we test each role separately and deliberately try to reach other people's data. Every login, data change and critical operation goes into an audit log with a timestamp, IP address and user ID. With Google or Microsoft sign-in, roles can come from the provider's groups through a mapping agreed with you. In a SaaS app, projects, files and API keys belong to the organisation, so a key created by an employee keeps working after they leave.
Why a hidden spreadsheet column is not a permission is covered in a panel instead of a spreadsheet, and roles in a custom panel on our panels and dashboards page.
Was this post helpful?